AWS Security Hub MCP App (Preview): Investigate Exposure Findings Inside Claude Desktop
Quick summary: On Jul 27, 2026, AWS launched the Security Hub MCP App preview: 8 read-only tools that bring exposure findings, attack paths, and remediation guidance into Claude Desktop at no additional cost for Security Hub customers.
Key Takeaways
- On Jul 27, 2026, AWS announced the preview of the AWS Security Hub MCP App, a local Model Context Protocol server that brings Security Hub exposure findings into Claude Desktop
- Chat investigates; EventBridge + Lambda (or your ticketing SLA) remediates
- How it fits next to other AWS agent surfaces Three different products are easy to confuse: 1
- Managed AWS MCP Server (GA May 6, 2026): general agent gateway to AWS APIs with IAM guardrails, CloudWatch, CloudTrail; 2 Regions at GA
- 2
Table of Contents
On Jul 27, 2026, AWS announced the preview of the AWS Security Hub MCP App, a local Model Context Protocol server that brings Security Hub exposure findings into Claude Desktop. Each tool call returns a dual response: a compact text summary for the agent to reason over, plus an interactive visualization (top exposures table, attack path graph, network path hops) you can verify in the same conversation.
The app is a read-only investigation surface for the exposure model Security Hub has been building through 2025 to 2026: correlated signals (vulnerability, misconfiguration, reachability, sensitive data) rolled into prioritized exposures, with impact analysis (Jul 6, 2026) feeding severity and attack-path scope.
Quantified scope (from AWS, not a customer claim): 8 documented tools; available at no additional cost to Security Hub customers; preview in all commercial Regions where Security Hub runs; requires Security Hub enabled with exposure findings already available.
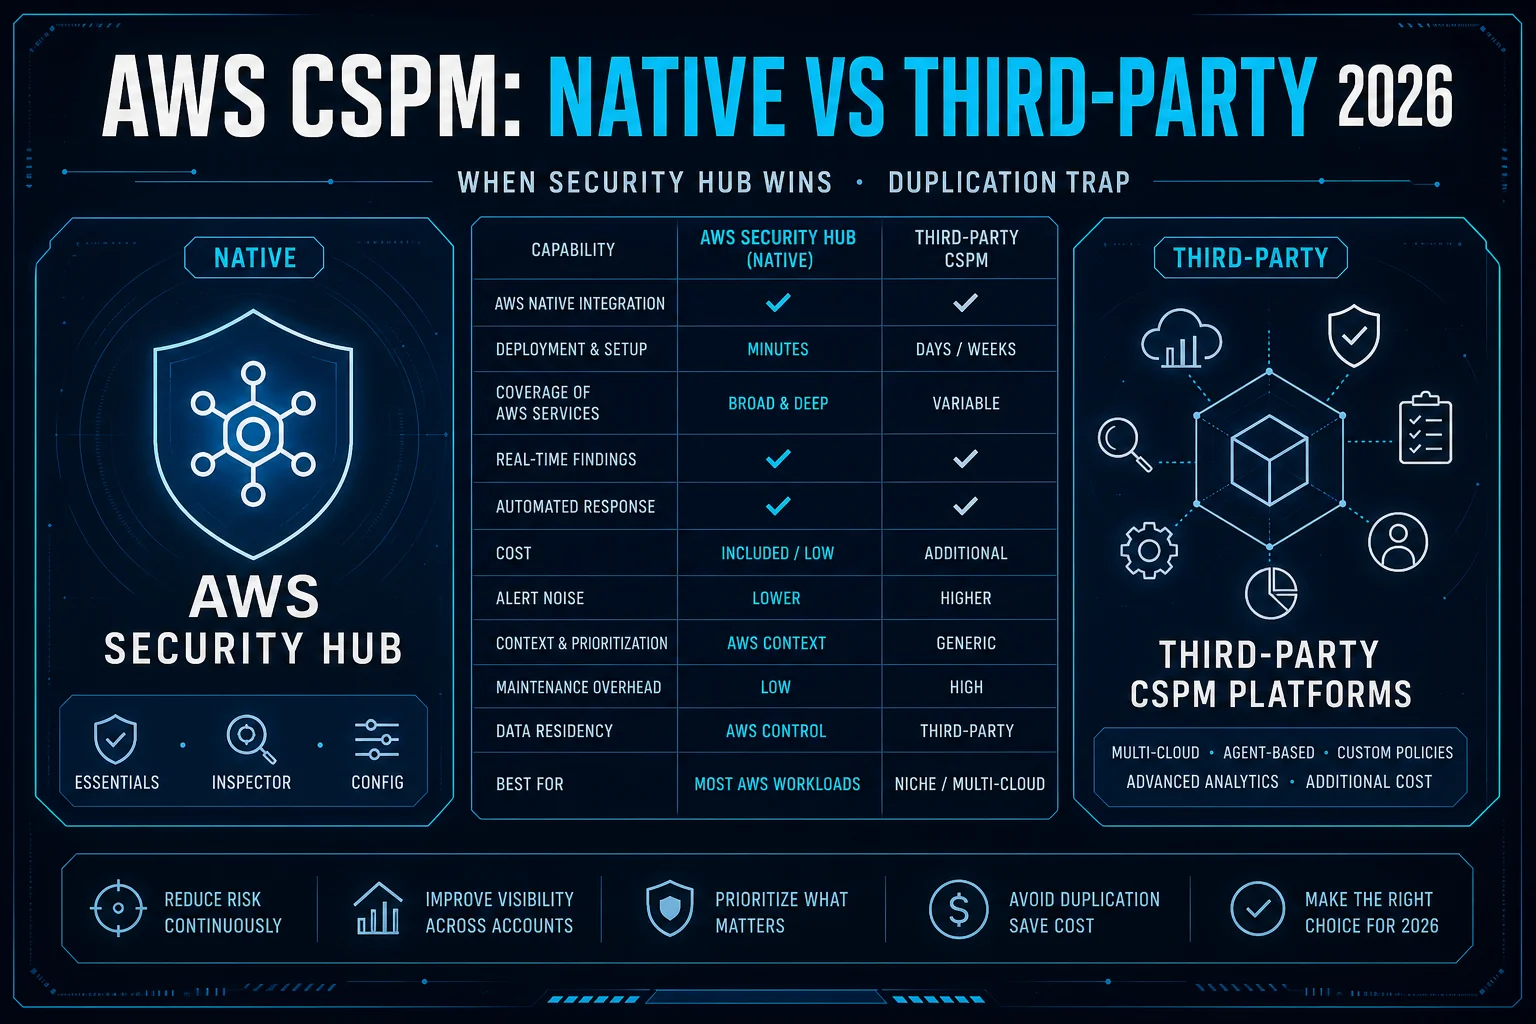
If you are still wiring Security Hub itself, start with our Security Hub compliance monitoring setup guide and the native CSPM vs third-party decision guide before chasing an MCP install.
Why this matters for security teams
Context switching is the tax most SOCs and cloud security engineers already pay: Security Hub console → Inspector → GuardDuty → Config → ticket → chat. The MCP App collapses the investigation read path into Claude Desktop without inventing a new finding store.
| Before | With Security Hub MCP App |
|---|---|
| Export finding IDs, paste into chat, lose graphs | Agent calls top_exposures / attack_path; UI renders in-chat |
| Attack path lives in one console tab | Graph + text summary in one dual response |
| Remediation docs hunted separately | recommendation returns guidance with doc links |
Opinionated take: treat this as an analyst accelerator for exposure triage, not as a replacement for automated remediation or incident response runbooks. Chat investigates; EventBridge + Lambda (or your ticketing SLA) remediates.
Trade-off: you gain speed and dual-response visualization inside Claude Desktop; you accept a local credential dependency, Claude Desktop-only install path in preview, and the reality that visualizations do not create audit evidence unless you capture outcomes into your ticket/IR system of record.
How it fits next to other AWS agent surfaces
Three different products are easy to confuse:
- Managed AWS MCP Server (GA May 6, 2026): general agent gateway to AWS APIs with IAM guardrails, CloudWatch, CloudTrail; 2 Regions at GA.
- Agent Toolkit for AWS skills/plugins: curated Agent Skills and install bundles for coding agents.
- Security Hub MCP App (this preview): Security Hub exposure investigation inside Claude Desktop with dual text + UI responses.
Recommendation: use the Security Hub MCP App when the question is “what are my top exposures and how are they reachable?” Use the managed MCP Server when agents need broader AWS API reach under organizational guardrails. Use AWS Security Agent full-repo review for codebase trust-boundary analysis, not for live cloud exposure graphs.
Concepts to know before the install
From the Security Hub MCP App user guide:
- Exposure finding: correlates multiple signals (vulns, misconfigs, reachability, sensitive data) into one view of a resource exposed to risk.
- Local MCP server: runs on your machine; uses your AWS SDK credential chain; holds no credentials of its own.
- MCP App: interactive UI rendered inside Claude Desktop (tables, graphs).
- Dual response: every tool returns agent text and a human-verifiable visualization.
Exposure quality still depends on the underlying Security Hub stack: Inspector, CSPM signals, network reachability, and (where enabled) impact analysis. An empty exposure backlog means an empty MCP conversation, not a broken install.
The 8 tools (call order matters)
| Tool | Job |
|---|---|
top_exposures | Interactive table of most urgent exposures. Call first; other tools need finding IDs from this list |
finding_detail | Overview + correlated-finding trait summary for one finding |
finding_overview | Text-only summary by finding ID |
correlated_finding_detail | Correlated findings for one trait (Vulnerability, Misconfiguration, Reachability, …) |
attack_path | Interactive reachability graph (resources, identities, services) |
network_path | Ordered hops from AWS edge → target (e.g. IGW → NACL → SG → ENI → instance) |
recommendation | Remediation guidance + documentation links |
resource_detail | Resource configuration by short ID (i-1234) or ARN |
Why this matters / who breaks without it: teams that skip top_exposures and invent finding IDs waste cycles on empty tool errors. Teams that stop at the table without attack_path / network_path miss the Jul 2026 impact story, since downstream privilege reach is often what turns a “medium” into a pageable risk.
Sample investigation flow (pilot worksheet)
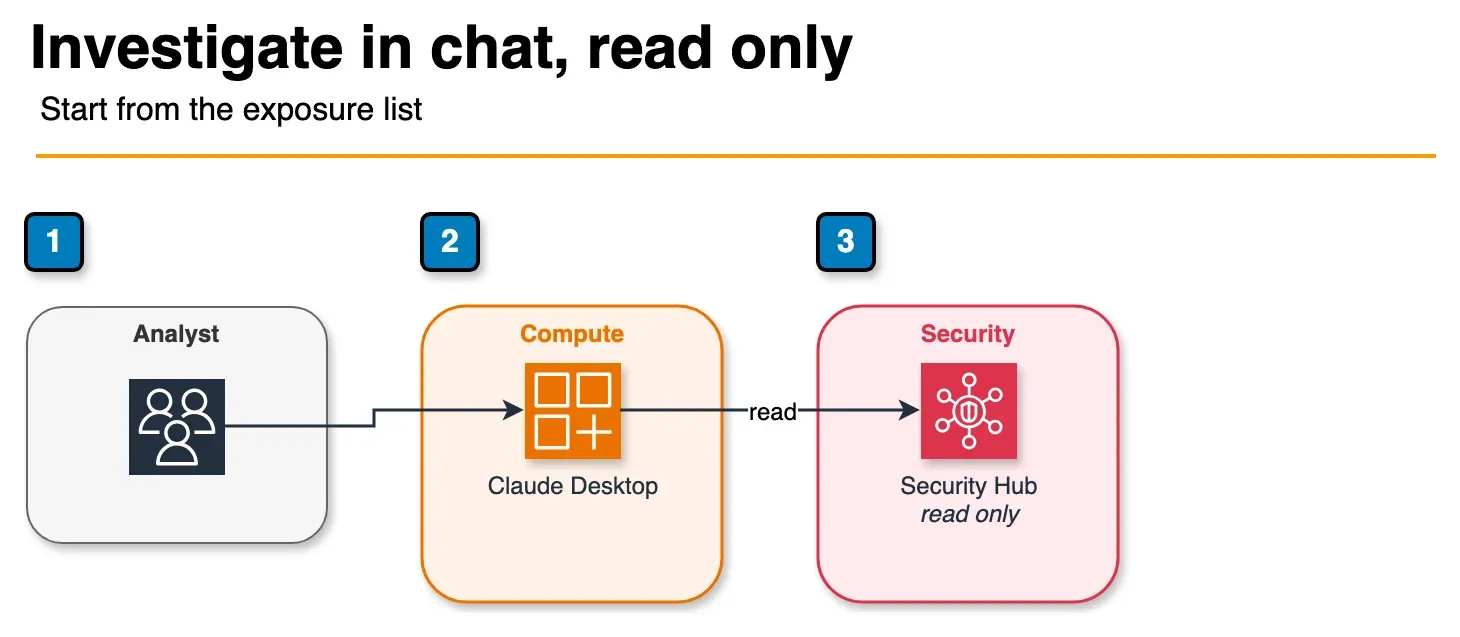
Figure: the pilot flow in the article. The analyst starts with the top exposures, then finding detail, attack path, and a recommendation. Every tool is read-only. Remediation stays in the existing change process. Finding ids are not shown. Open the draw.io source.
Use this sequence on one Critical exposure during the pilot. Do not batch-remediate from chat.
- Prompt: “What are my top security exposures?” → confirm
top_exposurestable loads and Region matches expectations. - Pick the top Critical →
finding_detail+correlated_finding_detailfor Vulnerability and Reachability traits. - Run
attack_pathandnetwork_path→ screenshot or export finding ID + hop summary into the ticket. - Call
recommendation→ map each suggested change to an owner and a change window (or to an existing EventBridge auto-remediation). - Optionally
resource_detailon the exposed instance/role/bucket → verify config matches what the path graph claims. - Close the loop outside Claude: ticket status, suppress/archive rules only when justified, and update the IR runbook if this class of exposure should page differently next time.
This worksheet is process guidance, not a published latency benchmark. If step 1 fails, fix credentials/Region/Security Hub enablement before debating prompt quality.
Prerequisites and setup
Prerequisites (AWS docs):
- AWS account with Security Hub enabled and exposure findings available
- Claude Desktop installed
- AWS credentials in the standard SDK credential chain
Before you install, confirm from a terminal:
# Assumed: AWS CLI v2 on PATH; SSO or profile already configured
aws sts get-caller-identity
aws configure get region
Install flow:
- Download the official bundle:
https://d29a07xw1myhp4.cloudfront.net/latest/sechub-mcp.mcpb - Open the
.mcpbfile. Claude Desktop starts the configuration flow; complete it. - Verify with a prompt such as: “What are my top security exposures?”
Failure modes and counter-cases
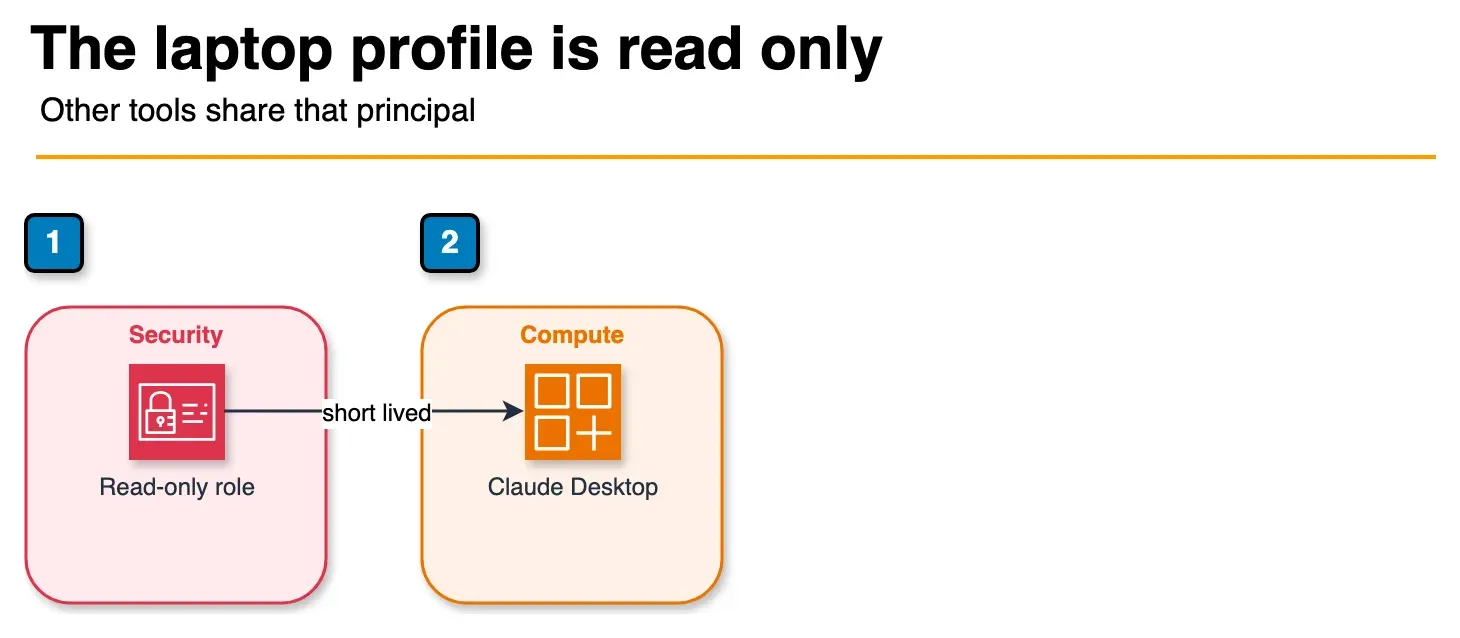
Figure: the credential rule in the article. Claude Desktop uses a short-lived read-only role. The Security Hub tools do not write, but any other client on that machine uses the same principal. A write-capable profile is how unrelated changes still happen. Open the draw.io source.
Other preview gotchas:
- No exposures yet → enable Security Hub standards / Essentials coverage and wait for exposure population before blaming MCP.
- Wrong Region in credential chain → findings look “empty” while another Region is full.
- Expecting remediation APIs → use
recommendationfor guidance, then your automated remediation path to execute.
What to do this week
- Confirm Security Hub readiness: delegated admin, Regions, exposure findings present (setup guide).
- Issue a read-only investigation role: SecurityAudit-class read + Security Hub read APIs; no
*:*on analyst laptops. - Install Claude Desktop +
.mcpbon one pilot workstation; runtop_exposures→attack_path→recommendationon a single Critical. - Write the outcome into your system of record: ticket or IR case with finding ID, path summary, and owner. Chat is not the archive.
- Decide the boundary: MCP App for human-in-the-loop investigation; EventBridge/Lambda for known auto-remediations; Security Agent for code; managed AWS MCP Server for broader agent API access.
If you only do one thing
Create a dedicated read-only AWS profile for Claude Desktop, install the official .mcpb, and walk one Critical exposure end-to-end (top_exposures → attack_path → recommendation) into a ticket. That one drill surfaces credential, Region, and process gaps faster than a policy memo.
What this post doesn’t cover
- Side-by-side latency or token-cost benchmarks of Claude Desktop vs console investigation (we have not published a first-party harness for this preview).
- MCP hosts other than Claude Desktop loading the Security Hub MCP App UI (unsupported in the Jul 27, 2026 docs).
- Org-wide rollout patterns (device management, DLP for finding text in chat logs, contractor laptop policy).
- Deep pricing math for Security Hub Essentials: see the CSPM decision guide.
For compliance program wiring beyond findings triage, see Cloud Compliance Services and AWS cloud security consulting.
Hardening Security Hub investigations? FactualMinds helps teams stand up Security Hub Essentials, exposure triage workflows, and agent guardrails without turning analyst chat into an admin shell. Talk to our team.
Frequently asked questions
When should we skip the Security Hub MCP App and stay in the console?
Does the Security Hub MCP App modify my environment or remediate findings?
How is this different from the managed AWS MCP Server (GA May 6, 2026)?
What could go wrong if analysts share a laptop AWS profile with write access?
Is there an extra charge for the Security Hub MCP App?
Which clients are supported in preview?
Agentic AI & Cloud Security
Works on making teams more productive with agentic AI. Writes the FactualMinds guides on AWS security and compliance: identity, threat detection, data protection, and audit readiness, the controls AI agents need before they touch production systems.
 Palaniappan P