Terraform vs CloudFormation on AWS (2026): Enterprise IaC Decision Guide
Quick summary: On a 40-account AWS Organization, platform baseline via CloudFormation StackSets (Hooks, GuardDuty enroll) plus app teams on Terraform/OpenTofu cut org-wide guardrail rollout from 9 weeks to 3, without forcing one tool for everything.
Key Takeaways
- AWS documents the pattern for baseline guardrails across OUs without per-account CLI runs
- Terraform 1.8+ and OpenTofu 1.8+ remain the default for application teams with existing modules and multi-provider needs
- This post compares Terraform/OpenTofu and CloudFormation/StackSets for enterprise AWS
- Benchmark pattern (not a cited client): 40-account AWS Organization, mixed Terraform app stacks + manual account baselines
- Platform team deployed StackSets (Config, GuardDuty, CloudTrail Hooks) to 3 OUs, and rollout went from 9 weeks to 3 weeks
Table of Contents
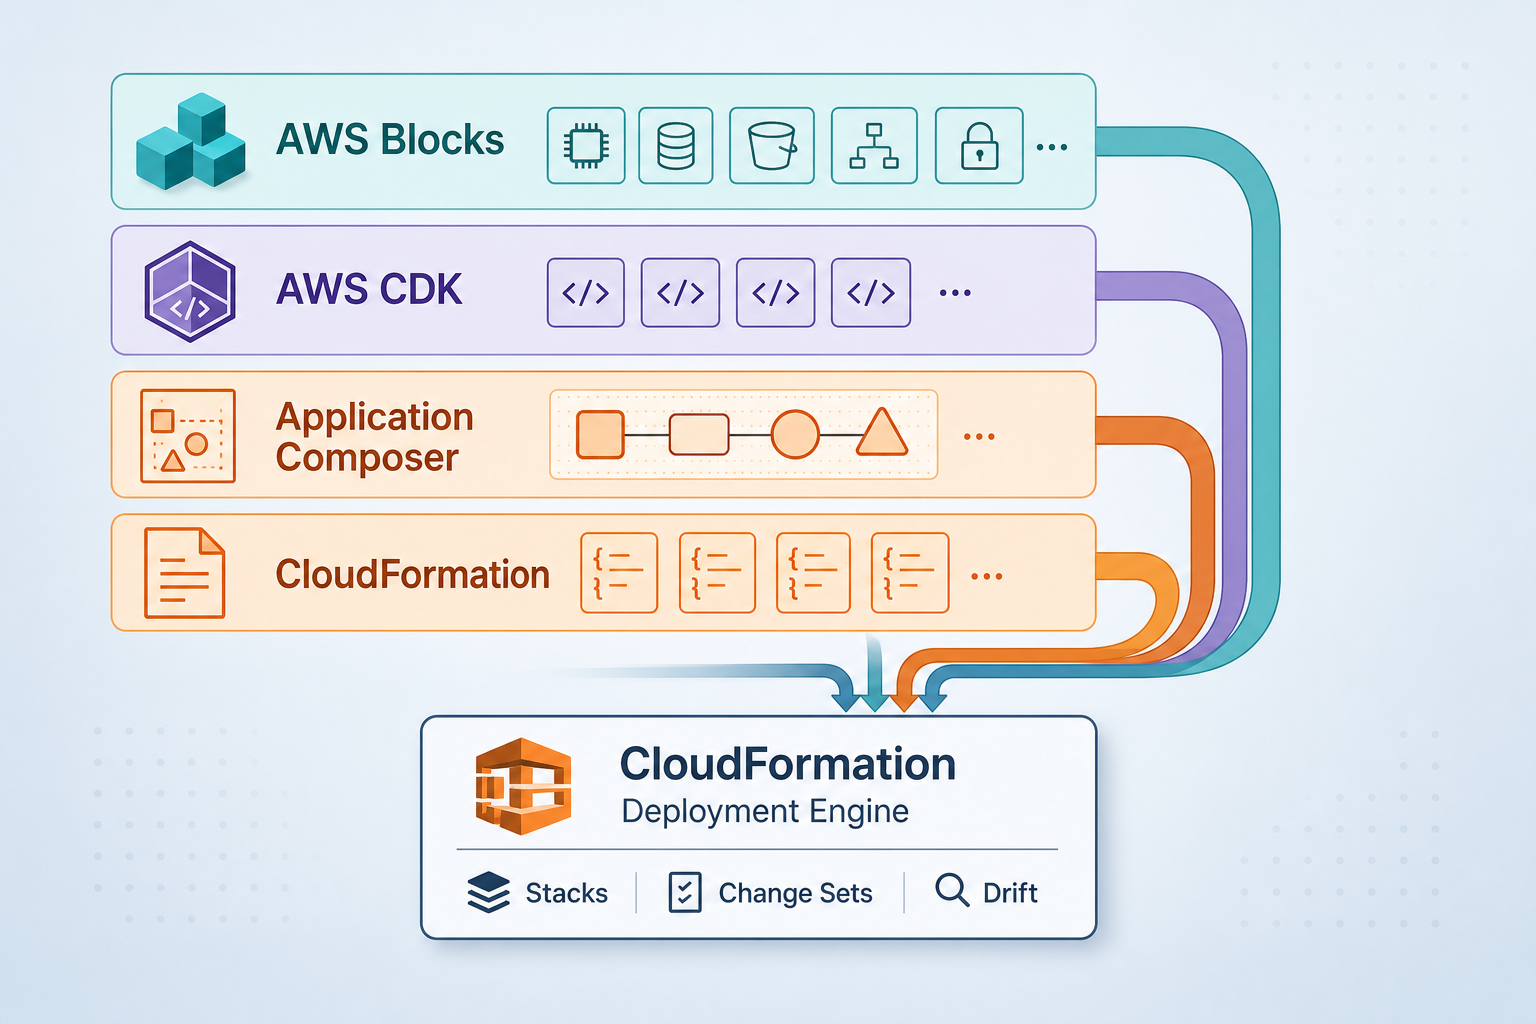
CloudFormation Hooks deploy org-wide via service-managed StackSets. AWS documents the pattern for baseline guardrails across OUs without per-account CLI runs. Terraform 1.8+ and OpenTofu 1.8+ remain the default for application teams with existing modules and multi-provider needs. The enterprise question is which layer each tool owns.
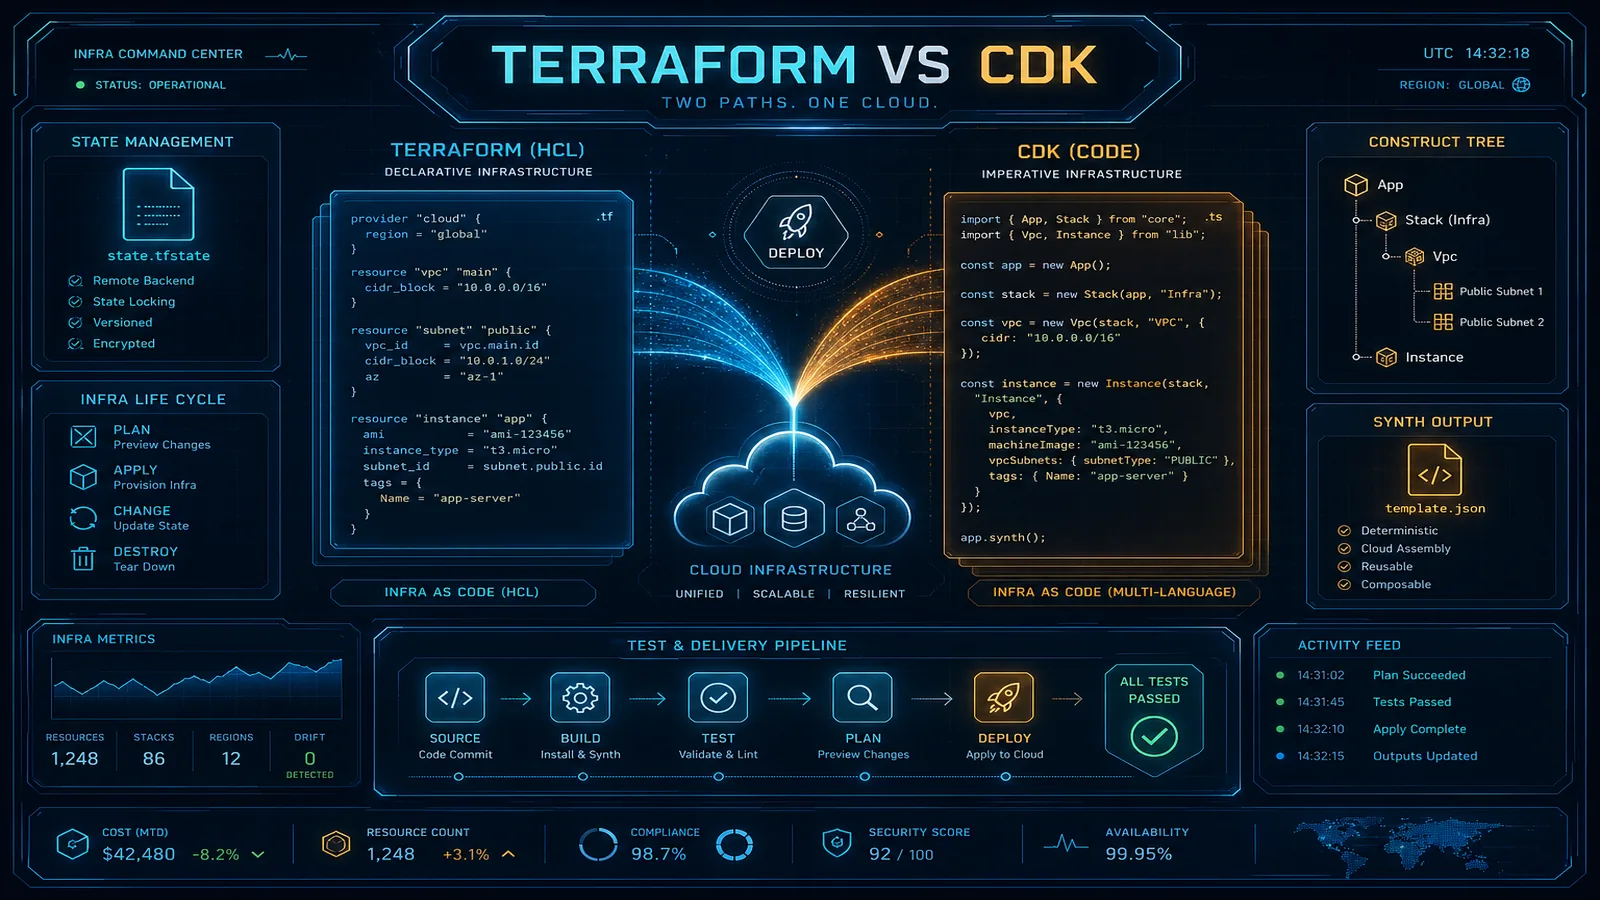
This post compares Terraform/OpenTofu and CloudFormation/StackSets for enterprise AWS. For authoring frameworks, see Terraform vs CDK. For language choice, see Terraform vs Pulumi. For CFN-only how-to, see CloudFormation best practices.
Artifacts: IaC decision matrix, enterprise criteria worksheet CSV.
Decision table
| Need | Terraform/OpenTofu | CloudFormation/StackSets |
|---|---|---|
| App team daily deploys | Default | Possible via CDK→CFN |
| Org-wide baseline | Secondary | Default |
| Multi-cloud / third-party providers | Default | Poor fit |
| No remote state ops | Weak | Default |
| GovCloud native packaging | Partition config | Stronger |
| Drift detection | CI + plan | Built-in stack drift |
Opinionated take: Hybrid. Use StackSets for the platform baseline and Terraform for application stacks. One-tool mandates fail when security needs org rollouts and apps need HCL velocity.
When CloudFormation and StackSets win
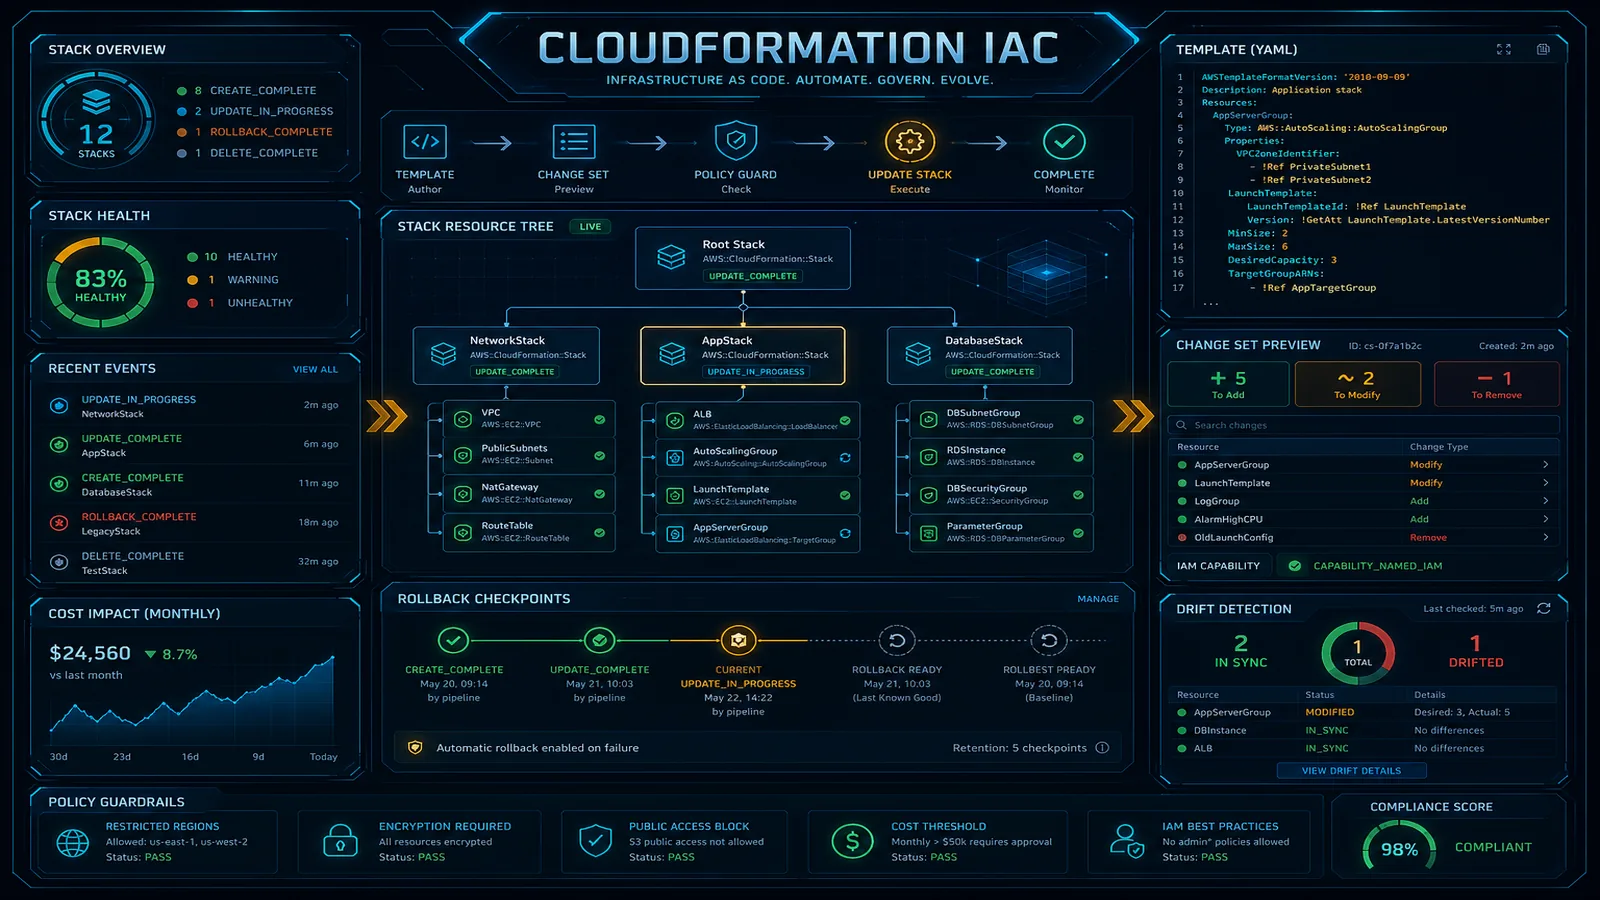
- Organizations auto-deployment: new accounts in OU get baseline stacks automatically
- CloudFormation Hooks: proactive compliance (e.g., S3 public access block) at deploy time
- No S3 state bucket: one less secret-leak surface
- Service Catalog integration for governed self-service
# Context: CloudFormation StackSet excerpt — service-managed permissions (July 2026)
# Deploy baseline to entire OU; enable trusted access in Organizations first.
Resources:
  GuardDutyEnable:
    Type: AWS::GuardDuty::Detector
    Properties:
      Enable: true
Platform team owns the template; member accounts receive stack instances without local Terraform.
When Terraform and OpenTofu win
- for_each / dynamic blocks for N environments without copy-paste YAML
- Terraform Registry modules shared across repos
- Multi-provider: AWS + Datadog + Cloudflare in one plan
- Existing estate: migration cost dominates the switch-to-CFN math
# Context: Terraform 1.8+, AWS provider ~5.x — app stack pattern
resource "aws_ecs_service" "api" {
  for_each = var.environments
  name     = "api-${each.key}"
  cluster  = aws_ecs_cluster.main.id
  # ...
}
What broke in the StackSets rollout
Hybrid reference architecture
Management account
├── StackSets (service-managed) → Config, GuardDuty, CloudTrail, Hooks
├── SCPs (Organizations)
└── Delegated admin for StackSets

Member accounts (app teams)
└── Terraform/OpenTofu → ECS, RDS, Lambda (remote state in shared account)
Align with enterprise governance OU taxonomy.
When NOT to use each
| Tool | Skip when |
|---|---|
| Terraform only | Org needs Hooks + auto-deploy to new accounts |
| CFN only | 500+ existing Terraform resources, multi-provider |
| CDK instead of both | Team wants neither TypeScript nor HCL (rare) |
What to do this week
- Score your org on enterprise-criteria-worksheet.csv.
- Run decision matrix and assign a platform vs app layer.
- If no StackSets baseline: pilot 2 accounts in one OU before org-wide.
- If Terraform state on S3: verify versioning + MFA delete + lock table today.
- Document the hybrid pattern in your internal wiki and end the “Terraform vs CFN” argument.
What this post doesn’t cover
- CDK authoring depth: Terraform vs CDK guide.
- Application Composer visual IaC: Application Composer post.
- Full Terraform state migration: state management guide.
- Pulumi: OpenTofu vs Pulumi.
Related: DevOps pipeline setup · Enterprise governance
Frequently asked questions
When should we use CloudFormation instead of Terraform on AWS?
When should we NOT standardize on CloudFormation only?
How does this differ from Terraform vs AWS CDK?
What breaks during org-wide StackSets deployment?
Does Terraform work in AWS GovCloud?
What could go wrong with Terraform remote state?
Enterprise AI Transformation
Enterprise AI transformation and implementation leader focused on pilot-to-production playbooks, with a background in financial services. Writes the FactualMinds guides on serverless, CI/CD, and DevOps on AWS, the delivery plumbing production AI depends on.